

Why the Board’s Question Has Changed from “Prevention” to “Survival”
Prepared by Hafsa Research and Analysis Company
The Core Shift: From Preventing Breaches to Surviving Them
The boardroom conversation has fundamentally changed. The question is no longer “What are you doing to prevent a breach?” It is now: “When a breach happens, what is your plan?”
The numbers behind this shift are sobering. Gartner’s 2026 survey found that 41% of CISOs reported at least one deepfake-related social engineering incident in the past 12 months, while 36% reported deepfake incidents during video calls. 79% of CISOs experienced phishing, spear-phishing, or business email compromise .
AI-driven fraud surged 1,200% in 2025, with losses projected to reach **$40 billion by 2027**—up from $16.6 billion in 2026 .
Security strategy is shifting from absolute perimeter defence to guaranteed breach survivability.
Solution 1: Move Identity Verification from “Detecting Fakes” to “Verifying Behaviour”
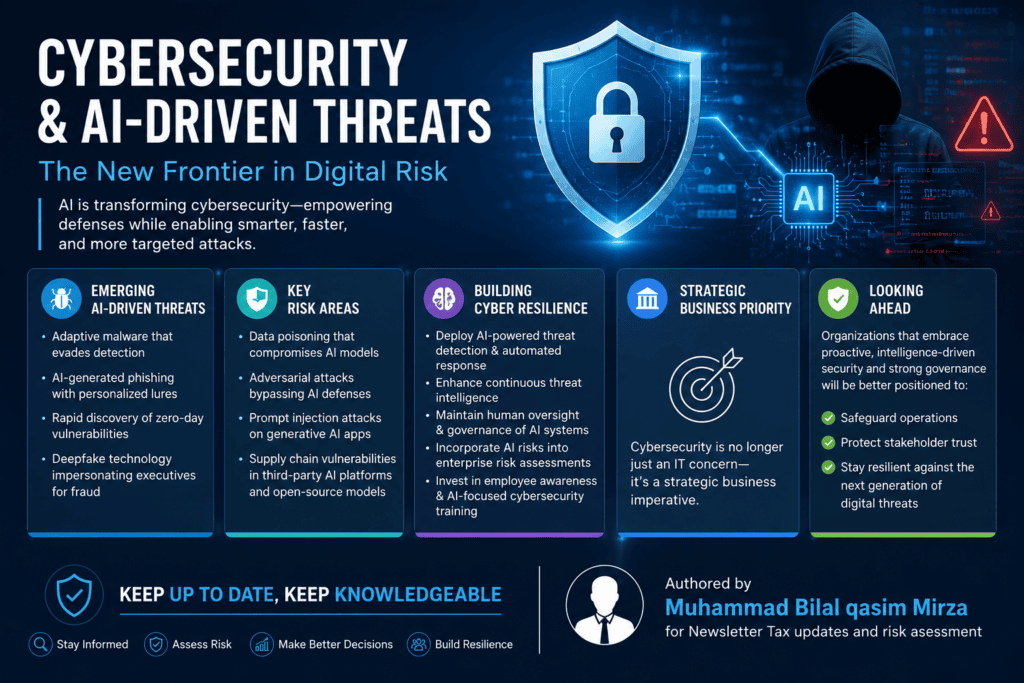
Gartner’s research reveals a critical problem: AI is degrading the reliability of traditional detection cues. Attackers can now combine phishing, BEC, synthetic media, and aggregated personal context across multiple channels.
Traditional training tells employees to “spot the fake.” That is no longer sufficient. Gartner recommends shifting to making security verification a standard behaviour for high-risk requests: training employees and approvers to pause, verify, and report high-risk requests—regardless of whether they arrive via email, voice, video, or AI app.
Implement phishing-resistant authentication and risk-based identity controls for high-value workflows (account recovery, privileged access, payment authorisation). Detect identity abuse after successful login or password reset.
Action step: Implement “multi-factor verification plus independent confirmation channel” for financial approval processes. Any request involving fund transfer must be confirmed through a second channel (e.g., callback to a known number). Do not rely on the authenticity of a single communication channel.
Solution 2: Fight AI with AI — From Prevention to Machine-Speed Response
Gartner is explicit: AI attacks are not novel, but AI significantly accelerates attack speed and scale. 87% of cybersecurity leaders ranked AI-related vulnerabilities among the fastest-growing cyber risks in 2025 .
Defence must operate at machine speed. Mani Sundaram, Executive Vice President at Akamai Security Technology Group, notes that the first fully autonomous AI ransomware campaign has been documented. AI agents can breach networks, move laterally, and execute attacks without human intervention.
The answer is AI-driven microsegmentation: automatically discovering application communication behaviour, mapping dependencies, and generating security policies in real time. When a breach occurs, microsegmentation immediately isolates the blast radius, allowing legitimate business to continue while blocking malicious lateral movement.
Action step: Assess whether your network relies on static firewall rules and VLAN isolation. If so, invest in AI-driven microsegmentation. Key metric: Is time-to-isolation measured in seconds, not hours or days?
Solution 3: Build Governance Frameworks for Agentic AI
Gartner identifies agentic AI governance as a top cybersecurity trend for 2026. No-code/low-code platforms and “vibe coding” have led to uncontrolled proliferation of AI agents, creating new attack surfaces and potential compliance violations.
The Five Eyes guidance on agentic AI offers practical recommendations:
- Maintain a structured inventory of all agentic AI deployments, including formally approved systems and informally adopted tools across departments
- Establish formal human approval workflows within 90 days for irreversible actions, PII access, production system modifications, and transactions exceeding thresholds
- Approval gates must be architecturally enforced, not reviewed after the fact—agents cannot bypass gates based on their own assessment of urgency
Action step: Inventory every AI agent and automation tool in your organisation. For each agent, document: identity, access scope, data sources, and whether it can execute irreversible actions. Any agent with write access to financial systems must have human approval gates and audit logs.
Solution 4: Put Post-Quantum Cryptography on the Roadmap
Gartner predicts that by 2030, quantum computing will render asymmetric encryption techniques currently relied upon by enterprises ineffective. Google’s 2026 white paper reduced the estimated resources required to break 256-bit elliptic curve cryptography by approximately 20x, requiring about 500,000 physical qubits to complete in minutes.
This is “Q-Day.” Attackers can execute “harvest now, decrypt later” attacks: intercepting encrypted data today, waiting for quantum computers to mature, then decrypting.
Gartner’s recommendation is clear: begin cryptographic asset inventories immediately, establish a crypto centre of excellence, align with vendors’ post-quantum roadmaps, and prioritise migration of long-lived assets.
Action step: Identify systems where data lifecycle exceeds five years. For financial records, customer data, and intellectual property, initiate post-quantum cryptography migration planning. Do not wait for the quantum threat to become reality.
Solution 5: Shift Security Culture from “Awareness Training” to “Adaptive Behaviour”
Gartner’s survey reveals that 57% of employees use personal generative AI accounts for work tasks, and 33% admit to entering sensitive information into unauthorised tools. This is the “shadow AI” problem—employees bypassing security boundaries to use external AI services for efficiency.
Traditional security awareness training has failed. Gartner recommends shifting to adaptive security behaviour and culture programmes, replacing generic awareness training with AI-specific practical exercises.
Action step: Launch an anonymous “shadow AI amnesty” policy to understand what AI tools employees actually use. Provide approved alternatives rather than simply prohibiting use. Incorporate security behaviour metrics (such as high-risk request verification rates) into departmental performance assessments.
Executive Checklist: AI-Era Cybersecurity Readiness
Governance:
- □ Establish AI governance committee including security, legal, compliance, and business representatives
- □ Inventory all agentic AI and automation tools, including shadow AI
- □ Implement architecturally enforced human approval gates for high-risk agent operations
Identity & Verification:
- □ Implement multi-channel verification for financial approval processes
- □ Deploy phishing-resistant authentication for high-value workflows
- □ Monitor for post-login identity abuse
Defensive Capability:
- □ Assess and invest in AI-driven microsegmentation
- □ Shift incident response from “prevention” to “survival and recovery”
- □ Establish agent behaviour logging integrated with SIEM
Encryption & Quantum Readiness:
- □ Conduct cryptographic asset inventory to identify quantum-vulnerable systems
- □ Initiate post-quantum cryptography migration planning
- □ Prioritise protection of long-lived sensitive data
People & Culture:
- □ Replace generic security awareness training with adaptive behaviour programmes
- □ Implement shadow AI amnesty policy with approved alternatives
- □ Incorporate security behaviour metrics into performance management
Closing Thought
2026 has been described by some experts as “the most dangerous year the internet has ever seen.” AI-driven attacks are surpassing traditional defensive capabilities in speed, scale, and personalisation.
Gartner’s conclusion is unambiguous: “The era of kicking unresolved cybersecurity vulnerabilities down the road is over.” AI-driven vulnerability discovery is becoming a top emerging risk for enterprises.
For CFOs and financial leaders, cybersecurity is no longer the exclusive responsibility of the IT department. Financial systems, payment processes, and customer data are primary targets. Security governance must become a core component of enterprise risk management.
The question is no longer “Will we be attacked?” It is “When an attack happens, will we survive?”
prepared by Hafsa Research and Analysis Company


